Assay collects compliance evidence from your live systems, read-only, keeps every record with its raw capture and a hash, and builds the audit pack for a certification or the proof pack for one client. It comes with our Virtual CISO service.
contact@araval.in · We reply within one working day.
An audit, a certification and every enterprise client’s security review ask for the same proof: how the cloud is set up, who has access, how changes are reviewed, which policies are in force. Most teams gather it by hand each time, as screenshots and exports.
Assay collects it from the systems themselves. Say a certification and it builds the audit pack. Say a client and it builds that client’s proof pack, with no other client in it.
Proof, not screenshots.
- Every check reads the real system, through read-only access: the AWS account, the code host, the live application.
- Each record keeps the raw output it was built from, with a SHA-256 hash, and says how to re-check it.
- Records are rendered by Assay from the stored data. No screenshots to take, crop or date.
- A quarterly sign-off is decided item by item and frozen by the approver’s signature.
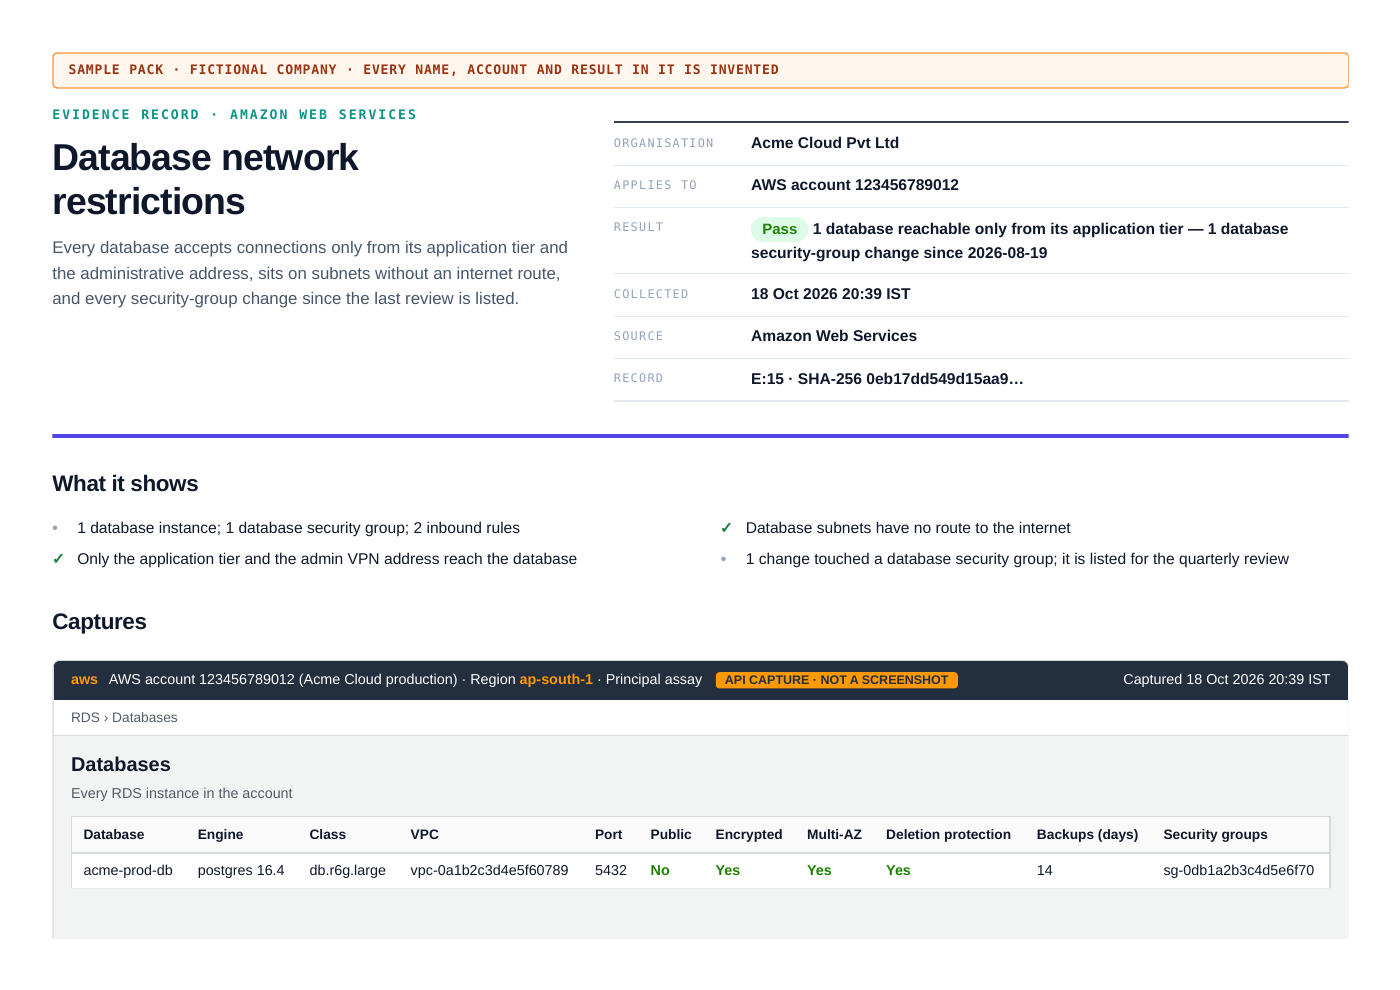
- 1 database, 1 database security group, 1 inbound rule
- Only the application tier reaches the database
- 46 security-group changes since the last review; none touched a database
rds describe-db-instances · ec2 describe-security-groups · cloudtrail lookup-eventsWhat it covers.
Evidence
- Read-only collectors for AWS accounts and each client’s environment, the application’s public URLs, Bitbucket, the pentest reports and access reviews
- Every run kept with its raw capture and a SHA-256 hash
- Collected every day, each check with its own freshness limit
Certifications
- ISO 27001:2022, SOC 2, DPDP Act 2023, ISO 42001, GDPR and ISO 27701
- Requirements mapped to controls through the Secure Controls Framework
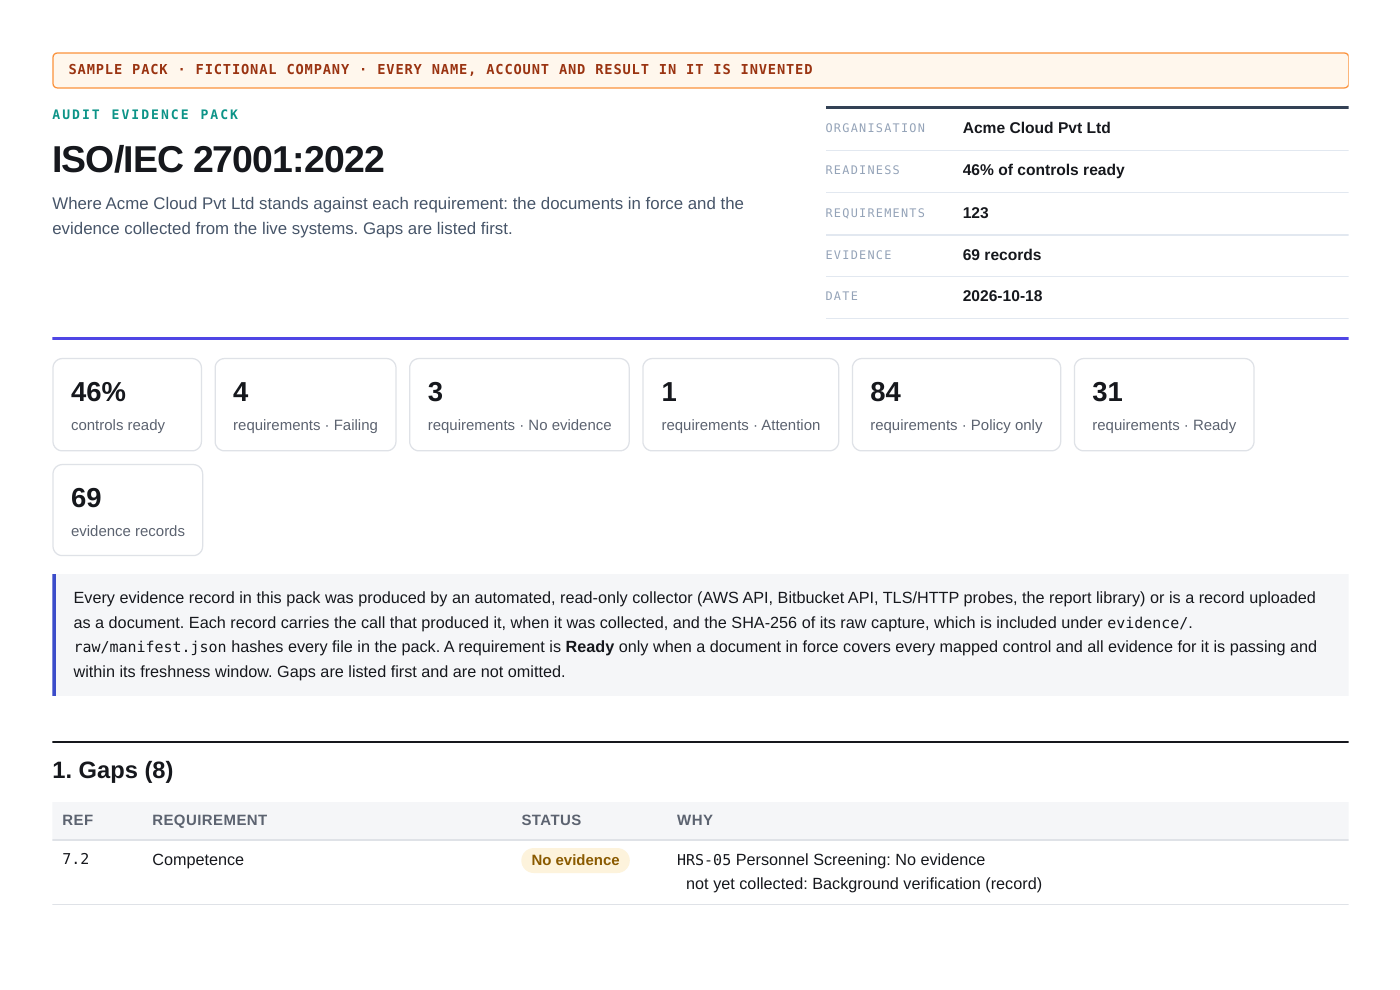
- Each requirement shown as ready, needing attention, failing or missing evidence, with gaps first
Policies
- A controlled-document workflow: draft, in review, approved, with nothing deleted
- First and major versions approved by someone who did not write them
- Approval signs a hash of the content, so text changed afterwards cannot be approved
Drafting with AI
- Claude reviews a policy against the evidence and drafts the next version
- Every statement cites an evidence record or a stated fact, or is marked unverified
- A draft cannot be submitted while anything in it is unverified
Packs
- An audit pack per certification: summary, gaps first, requirement table and Statement of Applicability
- A proof pack per client that names no other client: identifiers are masked and the build fails if one survives
- One bookmarked PDF, plus a zip with every raw capture and a manifest hashing every file
Quarterly sign-offs
- Threat intelligence: every GuardDuty finding since the last review, with Inspector and Security Hub
- Database network rules, one change traced from its ticket to production, and the DR drill’s RTO and RPO
- A decision on every item, then a signature; the signed PDF goes into the audit pack and to Scrut
A sample audit pack.
An ISO 27001 audit pack for a fictional company, built by Assay the way it builds a real one.
- The summary, gaps first
- The Statement of Applicability
- Evidence records with their captures
- A signed quarterly sign-off
- Policies in force, as controlled documents
PDF, 24 pages, 0.8 MB: an excerpt of the full pack. The company and every value in it are made up.
Evidence an auditor can re-check.
- Every record says where it came from, shows the data and gives the command that reproduces it.
- The collectors only read, and every run is kept, so last quarter’s evidence is still there next quarter.
- Approving a policy or signing a sign-off takes the approver’s typed name, checked against who may approve: a signature separate from signing in.
- A client’s pack never names another client.
Assay already runs the compliance evidence for a B2B SaaS company with enterprise clients.
It comes with our Virtual CISO service: we set it up with read-only access to your systems and run it with you.
Have an audit or a client review coming up? Talk to us about the evidence.
contact@araval.in · We reply within one working day.